← News
Topic · Product

Linux

21 articles

See also
📰

Latest Linux articles

Compromised MemTensor Packages Deliver sckit Credential Stealer via npm and PyPI

Compromised MemTensor Packages Deliver sckit Credential Stealer via npm and PyPI

Unknown threat actors have managed to compromise two legitimate MemTensor packages across the npm and Python Package Index (PyPI) repositories to push a platform-specific Go-based implant dubbed sckit designed for Windows, Linux, and macOS. According to reports from Aikido, SafeDep, Socket, and StepSecurity, the libraries in question below - @memtensor/memos-cloud-openclaw-plugin versions

Sep 23, 2026 · byThe Hacker News
Exploit Released for Unpatched Ubuntu Linux Flaw Enabling Host-Root Container Escape

Exploit Released for Unpatched Ubuntu Linux Flaw Enabling Host-Root Container Escape

A use-after-free in the Linux kernel's AF_UNIX socket subsystem can be used to escape a container and gain root on the host, security firm DepthFirst said in research published September 22. The flaw, tracked as CVE-2026-80521 (CVSS score: 7.8), was fixed upstream on August 6, but Ubuntu has not shipped the patch for its 26.04, 24.04, or 22.04 LTS releases. DepthFirst

Sep 23, 2026 · byThe Hacker News
Rabbit’s new AI agent doesn’t need an R1 to run

Rabbit’s new AI agent doesn’t need an R1 to run

Rabbit, the company behind the underwhelming R1 device, is rolling out a standalone AI agent that you don't need its hardware to use, as reported earlier by Wired. The startup says its new OS3 "agentic operating system" runs in the cloud but operates locally across Windows, Mac, and Linux devices. According to Rabbit, you can […]

Sep 22, 2026 · byThe Verge
New Linux Kernel Flaw Gives ARM64 KVM Guests Read-Write Access to Host Memory
New Linux Kernel Flaw Gives ARM64 KVM Guests Read-Write Access to Host Memory

A new flaw in the Linux kernel's KVM virtualization code for ARM64 processors can leave a freed piece of host memory exposed to a guest virtual machine on hosts with nested virtualization enabled. The bug, tracked as CVE-2026-89775, allows a guest to read and write host kernel memory, and the researcher who found it says it can be used to escape the guest and run code on the host machine.

Sep 22, 2026 · byThe Hacker News
CISA Flags Three Linux Kernel Vulnerabilities Exploited in the Wild

CISA Flags Three Linux Kernel Vulnerabilities Exploited in the Wild

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Friday added three security flaws impacting the Linux kernel to its Known Exploited Vulnerabilities (KEV) catalog, citing evidence of active exploitation. The vulnerabilities are listed below - CVE-2025-39682 (CVSS score: 9.8) - An improper check for unusual or exceptional conditions vulnerability in the TLS receive path

Sep 19, 2026 · byThe Hacker News
Public Exploits Released for Four Linux Kernel Flaws That Enable Local Root
Public Exploits Released for Four Linux Kernel Flaws That Enable Local Root

A security researcher has released working exploit code for four Linux kernel flaws that each let a local user gain root, the highest level of access on a machine. Kernel maintainers have fixed all four over the past few weeks, so a system running an up-to-date kernel is not affected. But the exploit code is now public, and any machine still running an older kernel should be updated. The flaws

Sep 18, 2026 · byThe Hacker News
Acronis cPanel Backup Plugin Vulnerability Exploited in Targeted Attacks

Acronis cPanel Backup Plugin Vulnerability Exploited in Targeted Attacks

Acronis has warned that a high-severity security flaw in its Backup plugin for cPanel and Web Host Manager (WHM) deployments has been exploited in the wild. The vulnerability, tracked as CVE-2026-87886 (CVSS score: 7.8), is described as a case of local privilege escalation due to insecure file permissions. It affects the following versions - Acronis Backup plugin for cPanel & WHM (Linux

Sep 16, 2026 · byThe Hacker News
BambooToken Malware Uses MQTT to Control Windows and Linux Systems
BambooToken Malware Uses MQTT to Control Windows and Linux Systems

Cybersecurity researchers have disclosed details of a multi-platform campaign that uses the Message Queueing Telemetry Transport (MQTT) protocol as a communication channel to control Windows and Linux systems. The emerging malware family, codenamed BambooToken, is assessed to be active since at least February 2023 and put to use in attacks targeting organizations across Asia and South America.

Sep 15, 2026 · byThe Hacker News
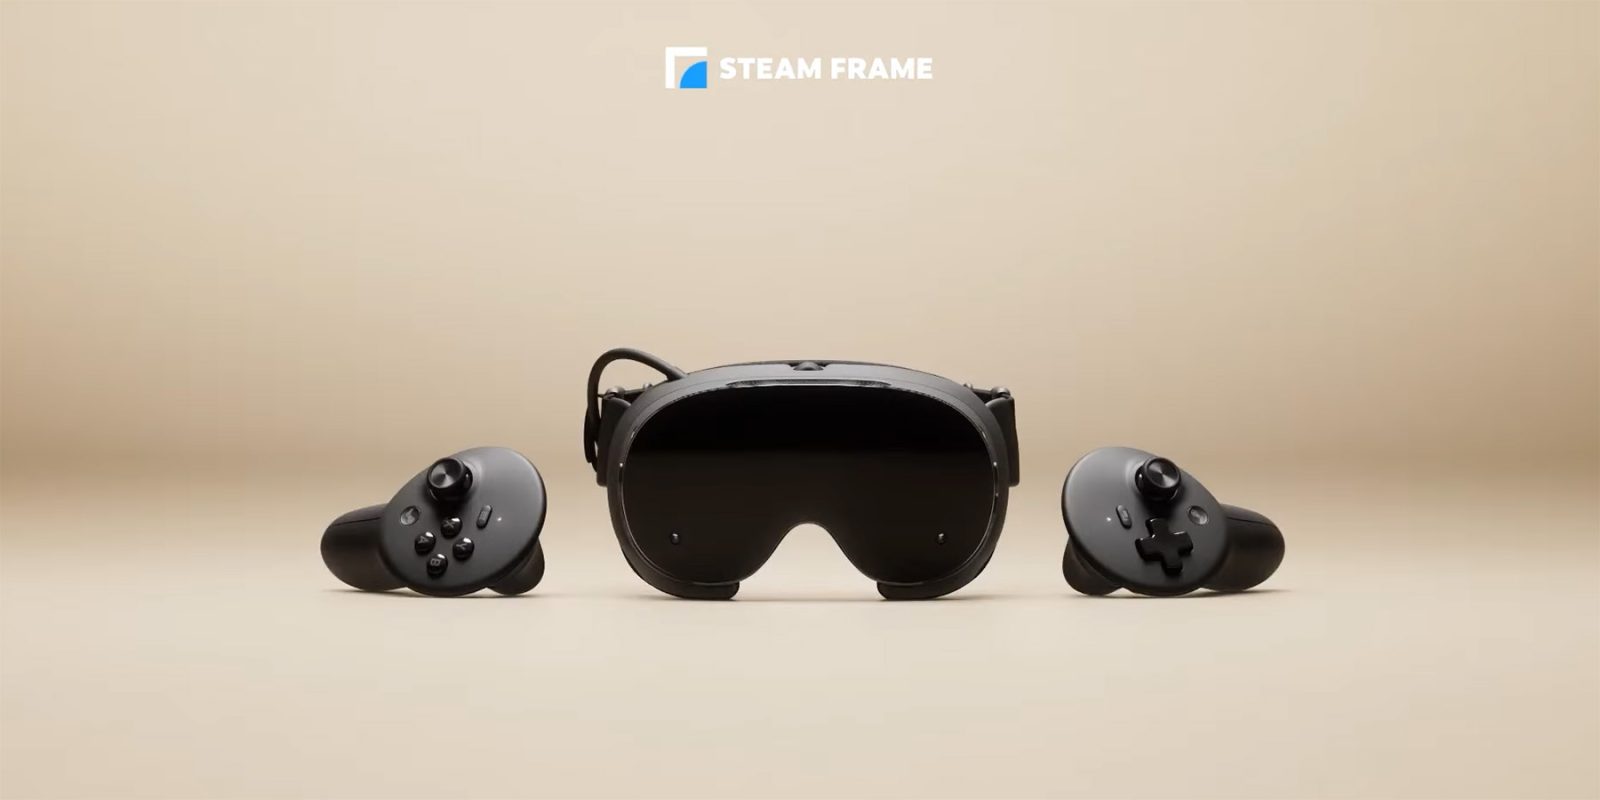
'It's Definitely at the Top of Our List' – SteamOS Is Getting Closer to Nvidia Driver Support

'It's Definitely at the Top of Our List' – SteamOS Is Getting Closer to Nvidia Driver Support

One of the biggest goal's of Valve's latest wave of hardware wasn't necessarily to move as many units as possible, but to expand the reach of SteamOS , and it does seem like it's succeeded. There are now two things that are really standing in Valve's way in its quest to dethrone Windows 11 as the de facto gaming OS: anti-cheat and Nvidia graphics drivers. And it looks like the latter is going to be solved soon. Ahead of Steam Frame's launch, I got a chance to sit down with Valve software developers Pierre-Loup Griffais and Jeff Leinbaugh , and I asked how Nvidia support was coming along. "Yeah, we're working on it hard," Griffais told me. "It's definitely at the top of our list. It's one of those things just like FEX and working on the Qualcomm driver, it just takes years." That doesn't sound like the driver support is right around the corner, but it does seem like the team has at least got Nvidia GPUs working on the Linux OS, albeit with limited performance. "We've done a few things like we've enabled the driver now in the main tree of SteamOS," Griffais told me, "so you can get things to light up on certain generations, but in terms of the performance difference between that driver and where the state of the art is, there's definitely still a little bit of a rift that we're trying to work on, but it's getting better day-to-day." There are certainly versions of Linux that already work with Nvidia drivers, but Team Green's GPUs are always a bit of a hassle on the open-source operating system. Instead, for most people, gaming on Linux works best with AMD graphics cards , as that company has supported drivers on the operating system for years. But for Valve's goal of getting as many people on SteamOS as possible, getting Nvidia's cards working at full performance is incredibly important. According to the latest Steam Hardware Survey , Nvidia GPUs still make up for 72.88% of Steam's player base. Getting Nvidia graphics cards up and running reliably on SteamOS would be a huge win for Valve. Hopefully Valve is able to get these graphics cards working as intended on SteamOS soon, and then, maybe, we can finally get anti-cheat support on the operating system. Because, after all, unlocking the operating system for another 72% of the playerbase could cause a huge spike in players migrating from Windows, and that'd be hard to ignore for the Call of Dutys of the world.

Sep 14, 2026 · byIGN
FreeIPA Flaw Chain Lets Anonymous Clients Create Reusable Administrator Credentials

FreeIPA Flaw Chain Lets Anonymous Clients Create Reusable Administrator Credentials

A flaw in FreeIPA lets a client that has never logged in create a Kerberos identity of its own choosing in the directory and end up in the administrators group, Red Hat says. FreeIPA is the system that determines who may log in across a Linux domain and maintains all identities in a 389 Directory Server database accessed via LDAP. The attack needs a second flaw in that database software. The

Sep 8, 2026 · byThe Hacker News